Why Authorization Management Deserves More Attention in Automated Workflows
Published: October 27, 2026
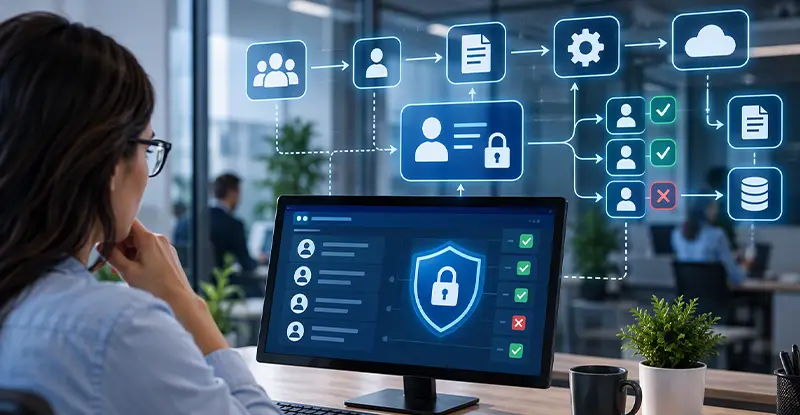
Businesses across Europe are automating document processing, invoice handling and approval chains at an accelerating pace. Yet many of those same organizations run their ERP systems with default permission sets that were configured years ago and never revisited. That disconnect creates a risk that no amount of clever automation can fix on its own.
When a company automates a purchase-to-pay workflow, the system executes tasks faster than any human team could. Speed, however, amplifies the impact of misconfigured access rights. A user who should only view purchase orders but can also approve them might never exploit that gap manually, yet an automated process could route sensitive transactions through that account dozens of times per day without anyone noticing.
Specialists in this space have been flagging the issue for years. The team at 2-Controlware in Breda, for instance, has spent over 17 years building authorization software specifically for Microsoft Dynamics 365 Business Central, helping organizations design, monitor and enforce user permissions within their ERP environment. Their focus on segregation of duties and conflict detection reflects a broader industry shift toward treating access governance as a core operational concern rather than a back-office afterthought.
Well-designed ERP permissions cannot prevent every error introduced by inconsistent incoming documents. docAlpha adds automated document classification, data validation, configurable routing, and human verification to document-driven processes.
Complement ERP authorisation controls with more consistent handling of business information.
Modern ERP platforms like Microsoft Dynamics 365 Business Central offer powerful automation capabilities out of the box. Organisations can set up approval workflows, automate journal postings and trigger notifications based on configurable business rules. But each of those automated steps relies on a user or service account that holds specific permissions.
The trouble starts when permission sets are too broad. An account used for automated invoice processing might carry permissions inherited from a template that was never trimmed down. In regulated industries such as finance, this can directly conflict with SOx requirements or GDPR obligations, and auditors reviewing these setups frequently find that user templates grant far more access than the actual process demands.
Recommended reading: Learn How Automated Approval Workflows Strengthen Transaction Controls
Segregation of duties, often abbreviated as SoD, requires that no single user can control all aspects of a critical business process. In a manual environment, this might mean one person creates a vendor record while another approves payments. Automation does not eliminate the need for that separation; it makes enforcement considerably more complex.
Consider an organisation where automated workflows handle everything from purchase requisitions to payment runs. If the service account driving those workflows has conflicting permissions, the entire chain lacks proper segregation. Tools that detect these conflicts at the configuration stage, before transactions flow through the system, prevent problems that are expensive to untangle after the fact.
Authorization solutions address this by offering continuous monitoring and conflict detection within Business Central. That kind of preventive control sits upstream of document processing automation and strengthens the integrity of every downstream step.
Automated purchase-to-pay operations still require clear checks before invoice approval and posting. InvoiceAction applies invoice validation, matching rules, and configured routing to support accountable AP workflows.
Reduce manual invoice handling without removing necessary finance review.
Broad authorization categories like "can edit sales orders" often miss the nuance that real compliance demands. Some fields within a record carry more risk than others. A discount percentage field or a bank account number field, for instance, should have tighter restrictions than a general contact name field.
Field-level security allows organizations to lock down specific data points without restricting access to entire pages or modules. Combined with validation rules that enforce data quality at the point of entry, this approach reduces errors that propagate through automated workflows. When a document processing system ingests data from an ERP, the quality of that data depends entirely on the controls applied at the source.
Organizations looking to strengthen their authorization posture can start with a permissions audit. Map every active user and service account against the tasks they actually perform, then compare that list to the permissions they hold. The gap between those two lists is your risk surface.
From there, implement user templates that reflect real job roles rather than convenience-based permission bundles. Review those templates at least twice a year, particularly after organizational changes or ERP updates.
Organizations that pair workflow automation with rigorous access governance tend to catch permission drift before it triggers audit findings or data incidents. The time spent mapping and monitoring authorizations now is a fraction of the cost of remediation after a compliance breach surfaces during an external review.
Recommended reading: Discover How Audit Trails Improve Control Over Automated Financial Workflows
 How Access Controls Secure Automated Business Workflows
 Automate Access Reviews Like You Did AP with AI in 2026
 Revolutionizing Access Control with AI: Innovations and Impact
 How to Defend Business Data Against Identity Based Cyber Attacks
 How AI and RPA Power Secure Digital Approvals
 IT Contractor Onboarding for Secure Document Automation Access

