Why Suppliers Are Now the Biggest Data Breach Risk
Published: October 20, 2026
NYC Health + Hospitals confirmed earlier this year that a breach at an unnamed third-party vendor had exposed the data of at least 1.8 million people. Nobody broke into the public health system directly. One of its suppliers got compromised, and all that damage rolled straight through to the organisation it served. This kind of thing has happened before, obviously, but 2026 has cranked the volume up to a point where it's hard to look away. The most dangerous way into your organisation probably isn't through your own network at all. It's through somebody else's.
The Verizon 2026 Data Breach Investigations Report puts the number at roughly 30% of all breaches now involving a third party, and in healthcare that figure climbs to nearly 48%. If your business depends on external vendors for payroll, file transfers, cloud storage, or software, those numbers should make you uncomfortable. Finance operations are closer to this risk than most teams realise, so let's see why that's the case and what you can actually do before a vendor's mess lands on your desk.
Supplier risk management requires businesses to understand how vendor information moves through their operations. When contracts, invoices, and supporting records are processed manually across departments, maintaining consistent workflows becomes more challenging. docAlpha automates document classification, information extraction, validation, and exception routing.
Reduce fragmented document processing and establish more consistent workflows for handling supplier-related information.
Frontal attacks on a company's own firewall aren't how most breaches happen anymore. Someone else leaves a side door open, and that's the way in. A payroll provider gets hit, and your employees' bank details are suddenly out in the wild. A file transfer tool gets exploited, and confidential financial documents end up where they shouldn't be.
The NYC Health + Hospitals case makes the point clearly enough, but the Oncology Institute breach that surfaced in May 2026 tells an even more unsettling story. That one traced back to a third-party software vendor, and the organisation only found out because Kroll, which administered the system on the vendor's behalf, flagged it. The company had no idea patient data had been accessed until someone further down the chain picked up the phone. You can pour money into your own security and still get burned by a supplier you've barely spoken to.
Recommended reading: Learn How to Validate Vendors Before They Put Your Business at Risk
Every vendor you add widens your attack surface. A mid-sized company will often rely on somewhere between 50 and 100 software providers, each with its own security standards, its own patching schedule, its own subcontractors, and its own appetite for cutting corners that you'll never know about.
Finance teams end up right in the middle of all this because they own or approve most of these relationships. They're the ones signing off on the payroll platform, the expense management tool, the accounts payable software, and the banking integrations. Every single one of those connections carries data that an attacker would love to get hold of, and every single one represents a failure point that's completely outside your direct control.
So the real question goes beyond "are our vendors secure?" and into territory that's far more awkward: "do we actually know which vendors hold our most sensitive data?" Most finance teams, if they're being honest, would say no.
Vendor risk gets assessed once a year at most companies, if it gets assessed at all. A security questionnaire goes out during onboarding, the responses come back, someone files them away, and nobody thinks about it again until the contract comes up for renewal. But a lot can change in 12 months. A key certification might lapse. A critical vulnerability might go unpatched for weeks. The vendor might quietly outsource part of its operations to a fourth party with far weaker controls than you'd ever accept.
That gap between reviews is where the real danger tends to build up. Tools like Vertice supplier risk management software track vendors' digital assets on an ongoing basis and flag changes in a supplier's security posture as they happen, which turns third-party risk from a yearly tick-box exercise into something much closer to live visibility. Ongoing monitoring like this matters because the breach that catches you out won't politely wait for your next quarterly review cycle to arrive.
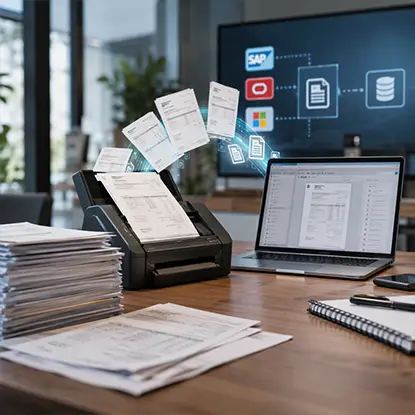
Businesses depend on multiple vendors and enterprise applications, making supplier document processing increasingly complex. docAlpha automates document capture, extraction, validation, and workflow processing while integrating with existing business systems.
Reduce repetitive data entry and streamline supplier document workflows without requiring a complete replacement of established enterprise applications.
If 2026's breach data has made anything obvious, it's that the perimeter has moved. Your organisation's real boundary isn't defined by your firewall or your office network anymore. It's the combined security of every supplier, subcontractor, and software provider that has access to your data. Finance teams, because of what they do every day, are right at the dead centre of that extended perimeter.
They manage the vendor relationships, approve the tools, process the payments, and handle exactly the kind of data that attackers want most. Taking ownership of vendor risk, building proper data maps, running due diligence on subcontractors, and pushing for continuous monitoring instead of annual tick-box reviews will all cut the chances of becoming the next company putting out a breach notice over something a supplier did.
The threat won't vanish completely, because third-party risk doesn't work like that. But the gap between organisations that get blindsided and those that respond quickly almost always comes down to one thing: how well they understood their supplier estate before the bad news arrived.
Recommended reading: Discover How Vendor Management Software Improves Supplier Visibility and Control
 Vendor Management Software
 Essential Steps for Businesses to Recover from a Data Breach
 Why IT Security and Tech Readiness Matter in Data Breaches
 Vendor Onboarding Workflow for Contractor Compliance
 How to Defend Business Data Against Identity Based Cyber Attacks
 CMMC POA&M Guide: Compliance Planning and Remediation Tracking

